
Security
Security, control by control.
The controls that keep each client separate, how each one is verified, and AAG’s certification and assessment program.
Controls
Controls and their evidence
| Control | What it does | Evidence |
|---|---|---|
| Per-client isolation | Each client’s gateway checks that a session belongs to it before any request runs. Cross-client requests are refused. | Automated tests of refusal in both directions. |
| Credential custody | Single-use intake. Encrypted with a dedicated key for that gateway. The control plane holds metadata only. Only that client’s connector can read the credential. | Storage is refused without the gateway’s dedicated key. Access is granted per credential. |
| Authorization before execution | Permission is checked against the exact operation before any provider call. Expired authorization refuses. | Automated tests, including expired authorization. |
| Audit evidence | Hash-chained records of when, which client boundary, who acted, the operation, the decision and the result. Queryable by client. | Chain verification tests. |
| Revocation and lifecycle | Suspend, retire and destroy gateways; rotate and revoke credentials. After committed revocation propagates, subsequent requests are refused. Already-admitted requests can complete. | Admission refusal measured against a 30-second bound; this is not an in-flight abort guarantee. |
| Infrastructure isolation | Client gateways run with their own runtime identities in their own cloud projects, provisioned by infrastructure-as-code with reviewed plans. Platform services sit inside a service-control perimeter. | Infrastructure code and reviewed plans. |
| Supply-chain controls | Container images are vulnerability-scanned, with builds blocked on high and critical findings. Software bills of materials and image provenance are recorded. | Release pipeline checks. |
| Backup and recovery | Point-in-time restore exercised against a real clone with integrity validation. | Restore drills. |
| Operational monitoring | Alerts for gateway availability, authorization errors, audit ingestion and repeated cross-gateway refusals. | Alerting exercised through a full alert, recover and clear cycle. |
Controls in context
Decide who can access what, and when.
These illustrations explain example policies and their boundaries. Use the evidence above to distinguish implemented controls from proposed workflow details.
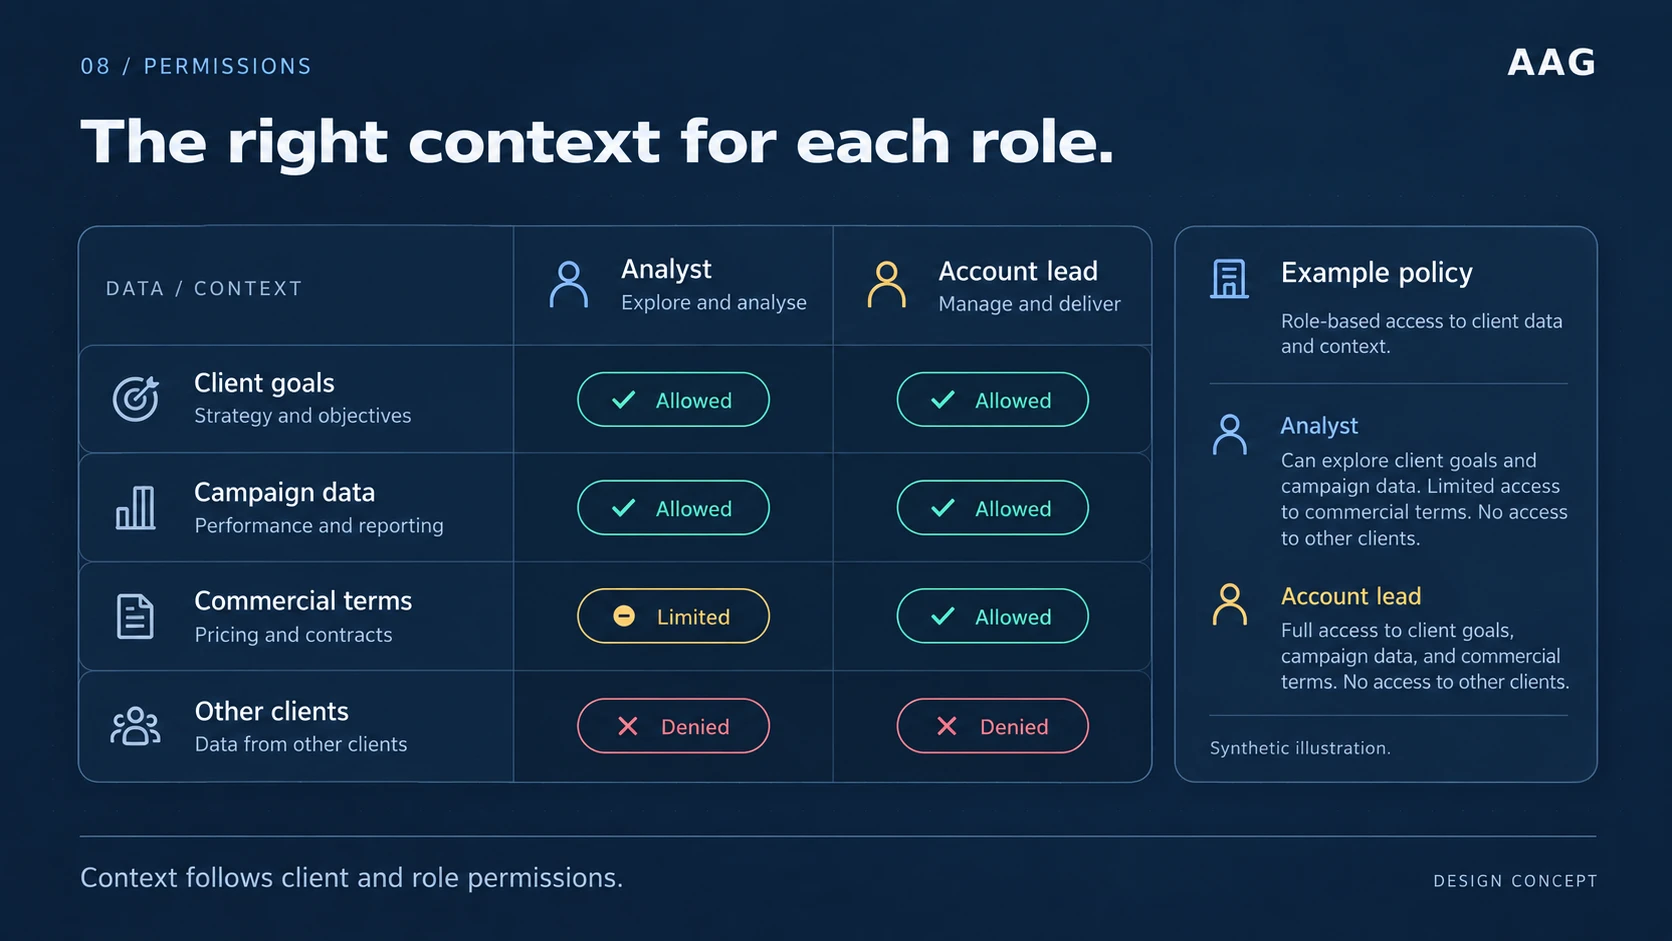
The right context for each role
View full size ↗Both example roles can read client goals and campaign data. The analyst has limited commercial access; the account lead has full commercial access. Neither can access other clients.
Synthetic policy example. Your agency defines the required roles and scope; verify the supported permission granularity during implementation. See the client boundary →
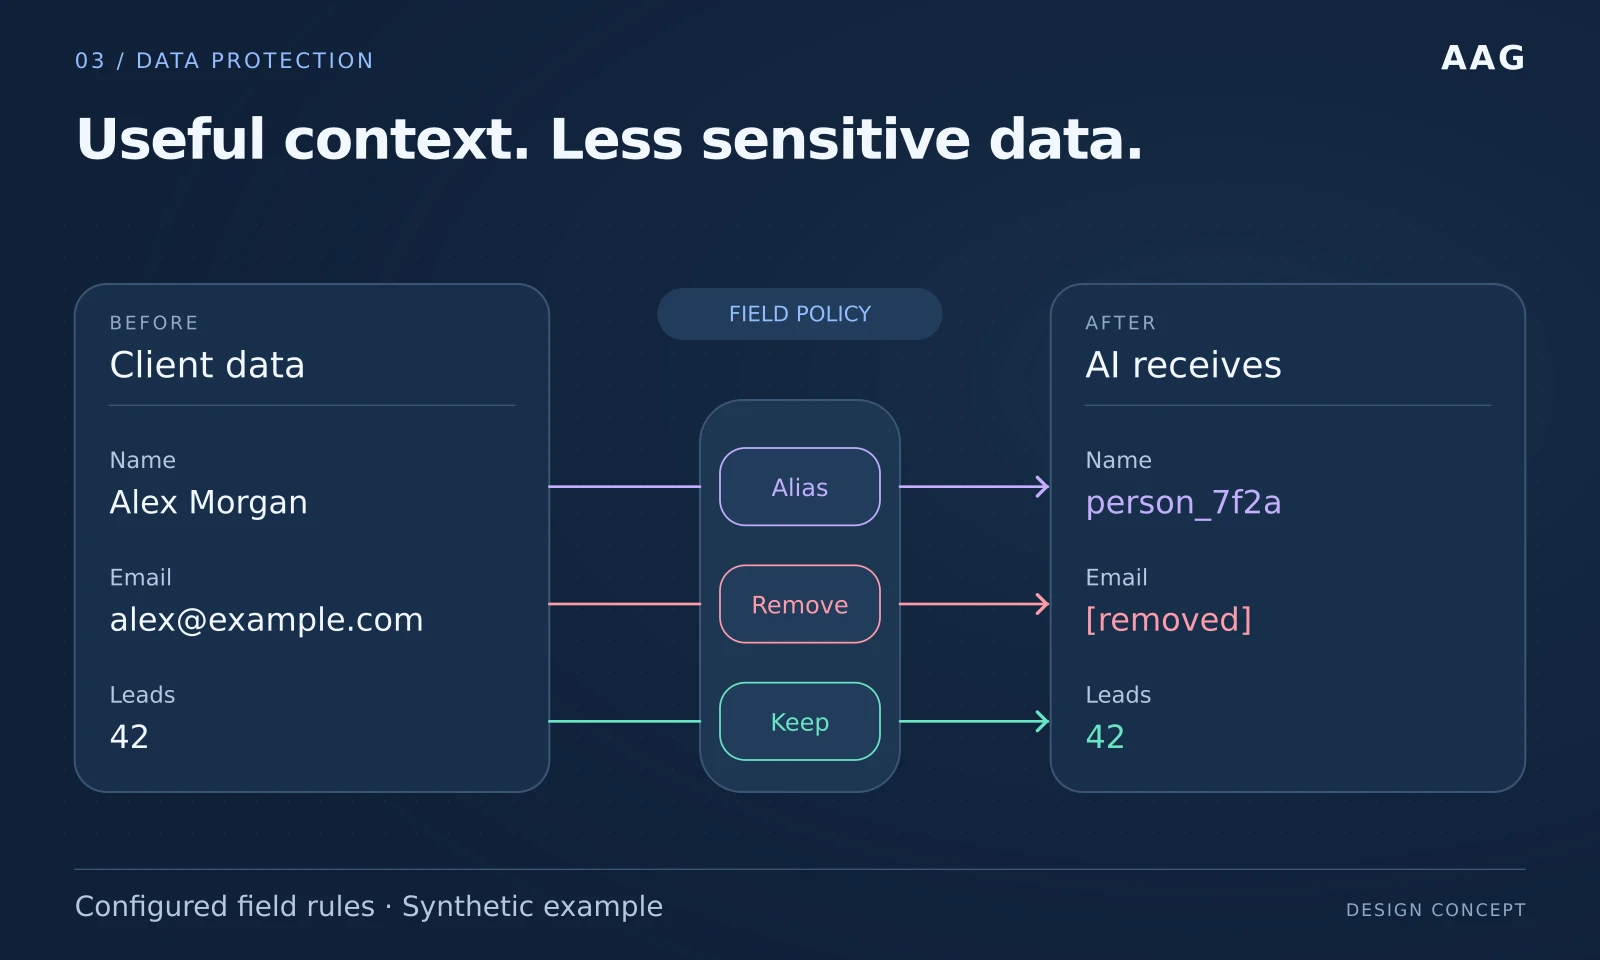
Useful context, less sensitive data
View full size ↗In this synthetic example, a name becomes an alias, an email is removed, and the useful aggregate remains. Field rules must be chosen for the data and operation.
Proposed field-policy example. Aliasing is not anonymization; confirm available transformations and their limits during scoping. Discuss data-handling requirements →
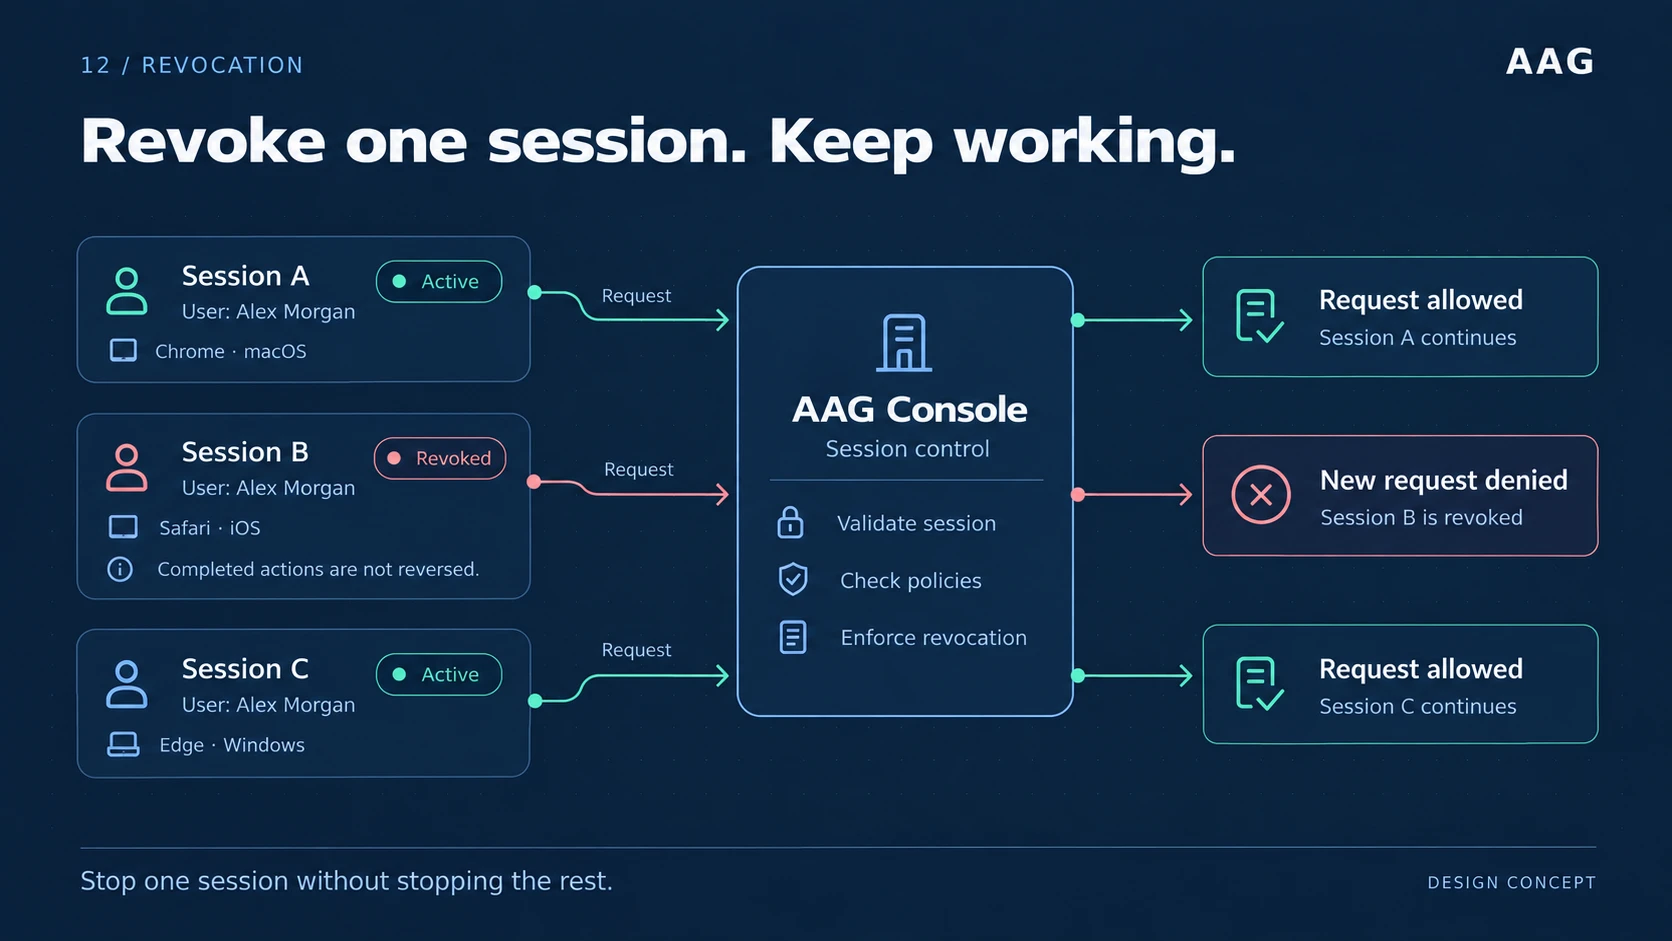
Revoke one session, keep working
View full size ↗Revoke access for the affected session while unrelated sessions continue. Previously completed actions are not reversed, and existing model context is not erased.
Conceptual session-control view. The console administers changes; gateways enforce them after propagation. The documented admission-refusal bound is 30 seconds, and already-admitted requests may finish. Read revocation boundaries →
Assurance
Certifications and assessments
- SOC 2
- Internal readiness inventory prepared.
- ISO/IEC 27001
- Current certification-program status available on request.
- Independent penetration test
- Scope prepared for an independent assessment.
Evidence before assurances
Internal readiness work and automated security tests are separate from an independent audit or certification. Ask us for the current engagement status and evidence relevant to your requirements.
Cloud-provider certifications do not certify AAG.
Posture
Contain first. Record decisions. Revoke quickly.
AAG’s security value is containment. A compromised or misbehaving AI session is limited to one client, rather than everything your agency can reach.
Every decision is recorded inside the client’s own boundary, and access can be revoked per client without touching the others.
For security reviewers
Bring the questionnaire
We will walk through your requirements, available evidence and any gaps to resolve.
Test the controls in a pilot
Cross-client refusal, revocation, audit contents: choose the properties that matter to you, and they become acceptance criteria.